Can a Self-Signed cert support an alias?
We are using self-signed certs on a private web network, and would like to know if it is possible to issue a self-signed certificate valid for multiple aliases?
For example, the FQDN of the server is apsmxgd-omrjts.devnet1.hill.af.mil, and we have an alias "jts.devnet1.hill.af.mil". We would, therefore, like a certificate to be valid for the following addresses:
apsmxgd-omrjts.devnet1.hill.af.mil
apsmxgd-omrjts
jts.devnet1.hill.af.mil
jts
Does anyone have instructions on how to create such a self-signed cert?
Thanks,
Dave
Accepted answer
If you believe that "Subject Alternative Name" can resolve your issue, you can add it when creating the self-signed certificate. Not sure which version of iKeyman you are using, but the one included in the CLM installation (server/jre/bin/iKeyman) has this option. It looks like this
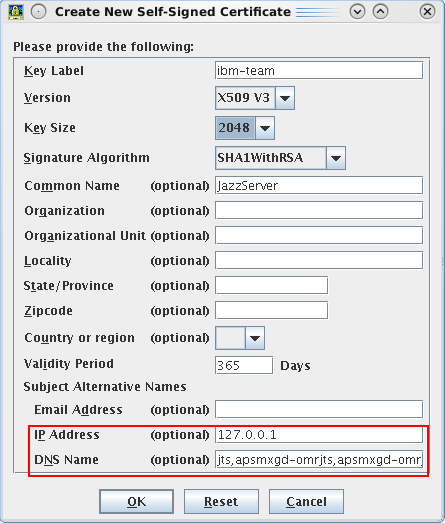
And the resulting certificate would look like this in Firefox.

If you have Java 7 installed, it's said that you can also use the keytool command with -ext option to add this property. I did not verify this though.
http://stackoverflow.com/questions/8744607/how-to-add-subject-alernative-name-to-ssl-certs
http://serverfault.com/questions/605843/unable-to-generate-certificate-with-subject-alternate-name-using-java-1-7-keytoo
And the resulting certificate would look like this in Firefox.
If you have Java 7 installed, it's said that you can also use the keytool command with -ext option to add this property. I did not verify this though.
http://stackoverflow.com/questions/8744607/how-to-add-subject-alernative-name-to-ssl-certs
http://serverfault.com/questions/605843/unable-to-generate-certificate-with-subject-alternate-name-using-java-1-7-keytoo
Comments
One other answer
It's my understanding that an SSL certificate can be used on multiple servers. In other words, you don't need to match the CN of the certificate to the FQDN of the server. That's why it never crossed my mind that "they will still receive an address mismatch warning for the cert". You can see a live sample by visiting the below website:
https://www.freessl.com/
Notice that the certificate is issued to "www.chainedssl.com".
In your case, all the certificate needs to do is to identify itself as "the server", whatever the CN you use for it does not matter.
https://www.freessl.com/
Notice that the certificate is issued to "www.chainedssl.com".
In your case, all the certificate needs to do is to identify itself as "the server", whatever the CN you use for it does not matter.
Comments
Comments
Donald Nong
Dec 04 '15, 2:33 a.m.Dave Evans
Dec 07 '15, 8:38 a.m.